



About this repository. Nexus-stride-gpt is where we collaborate on enhancements to mrwadams/stride-gpt. It holds STRIDE GPT with upstream's full git history, kept in sync with upstream's
master(the workflow guide explains how), plus the enhancement commits listed under Unreleased in the changelog. STRIDE GPT is © Matt Adams and released under the MIT License; see License.
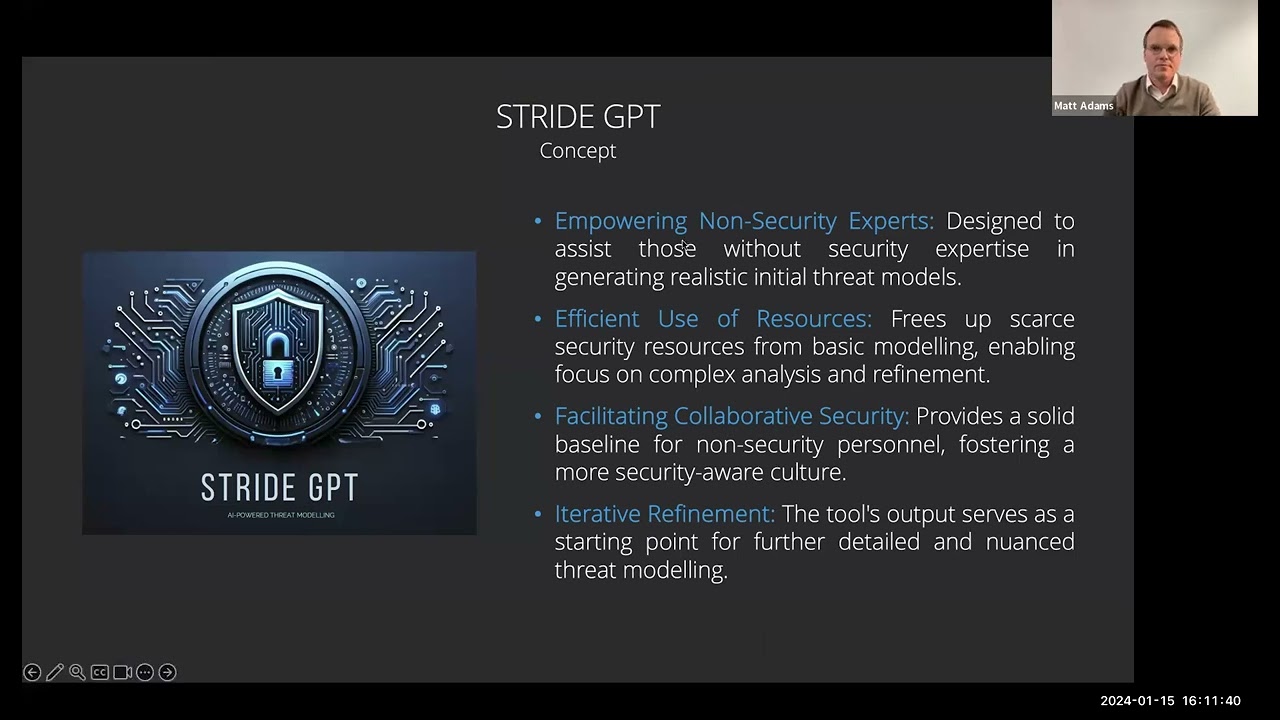
AI-powered STRIDE threat modelling. Point it at a codebase or describe an application — get a threat model with source-matched evidence, OWASP/MITRE annotations, 69 security controls, and compliance mapping to AIUC-1, ISO 42001, ISO 27001 and the EU AI Act.
For the Nexus enhancements, install from source. Published PyPI and Docker packages are upstream releases.
pip install -e .  # after cloning this repository
export ANTHROPIC_API_KEY=your-key        # or OPENAI_API_KEY, GOOGLE_API_KEY, ...
stride-gpt analyze ./my-app -o report.md # agentic codebase analysis
stride-gpt quick -i description.txt # single-shot from text- How it works
- Autonomy levels
- Features
- Installation
- Usage
- Sample output
- Security and privacy
- Documentation
- Contributing
- License
flowchart LR
    subgraph Input
        Code["Codebase"]
        Desc["Description, diagram<br>or GitHub repo"]
    end
    subgraph Agent["CLI agent (analyze)"]
        Plan["1 · Plan<br>classify app, pick subsystems"]
        Explore["2 · Explore each subsystem<br>read_file · grep · load_reference"]
        Synth["3 · Synthesise<br>cross-cutting threats"]
    end
    Quick["quick / web UI<br>single-shot"]
    Cards[("Reference cards<br>OWASP LLM and ASI · insider threat<br>MITRE ATT&CK and ATLAS<br>security and AI controls")]
    Catalog[("Control catalogue<br>AIUC-1 · ISO 42001<br>EU AI Act · ISO 27001")]
    Reports["Markdown · HTML<br>JSON · SARIF"]

    Code --> Plan --> Explore --> Synth --> Reports
    Desc --> Quick --> Reports
    Cards -. loaded on demand .-> Explore
    Cards -. loaded on demand .-> Quick
    Catalog -. deterministic lookup .-> Reports
- Plan. Architect model classifies the codebase and proposes 3–7 subsystems.
- Explore. Per-subsystem agent reads files, greps, and loads only the reference cards it needs (OWASP, MITRE, controls). Supplied snippets are checked against files; missing or unmatched evidence remains marked. A matching citation does not prove exploitability.
- Synthesise. One call finds cross-cutting threats that span subsystems, with evidence verification.
- Report. Control IDs the model chose are mapped to framework requirements by catalogue lookup, never by generation.
STRIDE-GPT uses the same six-level scale as Nexus-ShadowScan, from L0 Chatbot to L5 Fully Autonomous (shadowscan.autonomy/v1). It describes action authority, approval scope and initiation; it is not a severity score or a numeric crosswalk to another framework. Autonomy informs control selection alongside data sensitivity, permissions, impact and exposure.
| Level | Name | Behaviour and oversight |
|---|---|---|
| L0 | Chatbot | Answers only; no tools or actions. A person starts every exchange. |
| L1 | Copilot | Assists a person in their session: drafts, suggests or retrieves with read-only tools. The person performs or confirms every action. |
| L2 | Supervised | A person starts the run and approves each side-effecting tool action before execution. |
| L3 | Semi-Autonomous / Agentic Workflow | Bounded multi-step workflow or model-driven loop; approval at checkpoints, not per action. May be event-triggered. |
| L4 | High Autonomy | Model plans and acts in a loop with write or execution capabilities and no per-action approval; people supervise by exception. |
| L5 | Fully Autonomous | Self-started by event, schedule or another agent; write, execute or delegated capabilities with no approval gates; people only monitor. |
Report a level only when approval and initiation evidence support it. Tool access or credentials alone do not justify L2/L3, and unknown is not L0. A scheduled flow with checkpoint approval remains L3, not L5. Earlier STRIDE-GPT reports used different L1–L4 meanings: reassess their behaviour before comparing them with this scale. New model-output threats with a valid level carry autonomy_taxonomy: "shadowscan.autonomy/v1". This identifies the vocabulary, not verified evidence; loading a historical report does not add or change that marker.
The agentic AI controls baseline scales 14 controls (AGT-01 to AGT-14) by level. The AI Insider Threat lens treats agents L3+ as potentially untrusted insiders.
Analysis — Agentic codebase analysis with resumable runs, per-phase token budgets and run manifests. Evidence checks match supplied snippets against files; findings without verified evidence remain visible. Single-shot mode from text descriptions. AI/agentic pattern detection for RAG, multi-agent, code execution, tool/MCP ecosystems, persistent memory.
Controls & compliance — 69 controls in eight domains with deterministic framework mapping to AIUC-1, ISO 42001, EU AI Act, ISO 27001. Exports for GRC as CSV, JSON, SARIF. Browse with stride-gpt controls.
Outputs — Markdown, JSON, SARIF, self-contained HTML. MITRE ATT&CK/ATLAS IDs and canonical names validated against packaged catalogues; unlisted IDs are omitted. This checks identifier validity, not applicability. HTML reports show Mermaid source as text without loading remote scripts. SARIF imports into GitHub, GitLab, Azure DevOps, IDEs.
Models — OpenAI, Anthropic, Google, Mistral, Groq, DeepSeek, OpenRouter, LM Studio. Reasoning-model support. Two-tier routing: strong architect for planning, fast worker for exploration.
Web UI — Streamlit app with attack trees, mitigations, DREAD scoring, Gherkin test cases, draw.io editor, compliance tab.
| Framework | Usage | Source |
|---|---|---|
| STRIDE | Threat categories | Built in |
| OWASP Top 10 for LLM Applications (2025) | OWASP_LLM per threat |
genai card |
| OWASP Top 10 for Agentic Applications (2026) | OWASP_ASI per threat |
agentic card |
| AI Insider Threat | INSIDER_CATEGORY + autonomy level (L0–L5) |
insider_threat card |
| MITRE ATT&CK Enterprise (v17.1) / ATLAS (2026.05) | Technique IDs, catalogue-constrained | mitre_* cards |
| Control catalogue (69 controls) | CONTROLS IDs per threat |
security_controls, ai_controls cards |
| AIUC-1, ISO 42001, EU AI Act, ISO 27001 | Deterministic lookup from controls | Catalogue |
PyPI packages are upstream releases. Install this checkout to use Nexus enhancements.
pip install stride-gptgit clone https://github.com/aisecnomad/Nexus-stride-gpt.git && cd Nexus-stride-gpt
uv sync # or: pip install -e .
cp .env.example .env # add your API keysdocker compose up # hardened: cap_drop ALL, no-new-privileges, read-only rootfs, resource limits# Agentic codebase analysis
stride-gpt analyze .
stride-gpt analyze ./my-app --worker-model anthropic/claude-sonnet-5 -y
# Output formats
stride-gpt analyze . -o report.json -f json
stride-gpt analyze . -o report.sarif -f sarif
stride-gpt analyze . -o report.html -f html
# Single-shot from text
stride-gpt quick -i app-description.txt
echo "A web API that processes payments..." | stride-gpt quick
# Interactive REPL
stride-gpt
# Browse controls and export compliance mapping
stride-gpt controls
stride-gpt controls --report saved-report.json -o mapping.csvCost note: Agentic analysis makes many LLM calls. Set spending limits with your provider first. Use
--max-llm-callsto cap per-subsystem calls (default 25).
All CLI flags
| Flag | Description |
|---|---|
--worker-model |
Default-tier model (e.g. anthropic/claude-sonnet-5) |
--architect-model |
Stronger model for planning/synthesis |
--no-architect |
Skip the architect tier |
--app-type |
Override detection: auto, web, genai, agentic |
--max-llm-calls |
Cap LLM calls per subsystem (default 25, 0 = unlimited) |
--max-tool-calls |
Cap code exploration calls (0 = unlimited) |
-o, --output |
Save report to file |
-f, --format |
markdown (default), json, sarif, html |
-i, --input |
Read description from file (quick only) |
-y, --yes |
Auto-approve the analysis plan |
Each tier also accepts --worker-api-key / --worker-api-base / --worker-max-tokens (and --architect-* equivalents). Run stride-gpt analyze --help for the complete list.
REPL commands and shortcuts
| Command | What it does |
|---|---|
/analyze [path] |
Analyze a codebase |
/quick |
Quick threat model from text |
/reports |
List previous reports (/reports <n> views one) |
/config |
View or change settings |
/help |
Show all commands and flags |
/quit |
Exit |
| Key | Action |
|---|---|
Tab |
Complete commands and file paths |
Up/Down |
Scroll history |
Right/End |
Accept suggestion |
Ctrl+L |
Clear screen |
Ctrl+C/D |
Exit |
Structured intermediates
When -o <path> is used, three JSON siblings are written alongside the report:
| File | Contents |
|---|---|
<stem>.plan.json |
Analysis plan: subsystems, focus areas, detected app type |
<stem>.findings.json |
Per-subsystem findings, cross-cutting threats, DFD |
<stem>.run.json |
Run manifest: models, timing, token usage, references loaded |
A subsystem's outcome is completed, budget_exhausted, parse_failed, error or skipped. File paths in manifests are redacted for safe sharing.
streamlit run apps/web/main.pydocker run -p 8501:8501 --env-file .env mrwadams/stridegptBefore exposing the UI, put it behind TLS and an identity-aware proxy. See Deployment hardening.
Sample markdown threat model (click to expand)
# STRIDE Threat Model: acme-payments-api

> Generated by STRIDE-GPT on 2026-07-16T09:42:00Z

## Authentication & Authorization

### Threats

| Threat Type | Scenario | Potential Impact | MITRE ATT&CK | Controls | Evidence |
|-------------|----------|------------------|--------------|----------|----------|
| Spoofing | An attacker forges a JWT using a weak or leaked signing secret to impersonate another customer. | Full account takeover and unauthorized access to stored payment methods. | T1550.001 | IAM-05, DAT-06 | app/auth/jwt.py:14-19 |
| Elevation of Privilege | A standard user calls an admin-only refund endpoint that only checks authentication, not role. | Unauthorized refunds and financial loss. | T1068 | IAM-07 | app/auth/dependencies.py:31-38 |

## Cross-Cutting Threats

| Threat Type | Scenario | Potential Impact | Controls | Affected Subsystems |
|-------------|----------|------------------|----------|---------------------|
| Denial of Service | No rate limiting lets an attacker exhaust the processor quota and DB connections. | Legitimate payments fail. | APP-08, NET-06 | Auth, Payments |

## Controls & Compliance Mapping

| Control | Name | Domain | Threats |
|---------|------|--------|---------|
| IAM-05 | Secure JWT issuance and validation | Identity & Access Management | 1 |
| IAM-07 | Deny-by-default, object-level authorisation | Identity & Access Management | 1 |

### ISO/IEC 27001

| Reference | Requirement | Controls |
|-----------|-------------|----------|
| A.5.15 | Access control | IAM-07 |
| A.8.5 | Secure authentication | IAM-05 |- Your code goes to the LLM provider you choose. For sensitive systems, use a local model or a provider with suitable data-handling terms.
- The agent reads the codebase you point it at. File tools are sandboxed to the target directory and refuse VCS metadata (
.git,.hg,.svn). - API keys are credentials. Keep them in env vars or
~/.stride-gpt/.env, never in version control. - Threat models are sensitive. A report is a map of your weaknesses: store and share it like one.
- Team deployments need hardening. See Deployment hardening.
Dependencies are pinned in uv.lock, scanned with Bandit, CodeQL, pip-audit, Gitleaks and Trivy. Use the security policy to route a private report to the maintainers of the affected code.
stride-gpt/
├── stride_gpt/              # shared library + CLI
│   ├── agent/               # agentic engine: planner, loop, tools, evidence
│   └── core/                # LLM abstraction, prompts, schemas
│       ├── controls/        # control catalogue + framework mapping
│       └── prompts/threat_model/  # reference cards (OWASP, MITRE, controls)
├── apps/web/                # Streamlit web UI
├── docs/                    # guides and generated references
├── tests/                   # pytest suite (~1.5s, zero real LLM calls)
└── pyproject.toml           # web UI deps in the `web` dependency group
| Guide | Covers |
|---|---|
| Architecture | Components, agent phases, data flows, trust boundaries |
| Controls and compliance | How threats map to controls and frameworks |
| Control catalogue | All 69 controls with guidance and mappings |
| Framework crosswalks | Coverage per framework |
| Agentic AI controls | Control baseline scaled by autonomy level (L0–L5) |
| Deployment hardening | Identity, encryption, network, logging |
| Operationalization | Custom controls, CI/CD patterns, enterprise deployment |
Pull requests welcome. See CONTRIBUTING.md for setup and conventions.
STRIDE GPT is released under the MIT License, Copyright (c) 2024 Matt Adams. This repository's top-level LICENSE is the Apache License 2.0; see NOTICE.